Security assessment
Review applications, infrastructure and working practices to identify exposure and set priorities.
Run & protect
Panlab helps organizations assess and protect applications, cloud environments and connected infrastructure. We combine security testing, risk and governance work with monitoring and response planning, so findings lead to practical action.
Protection planned around your applications and operations.
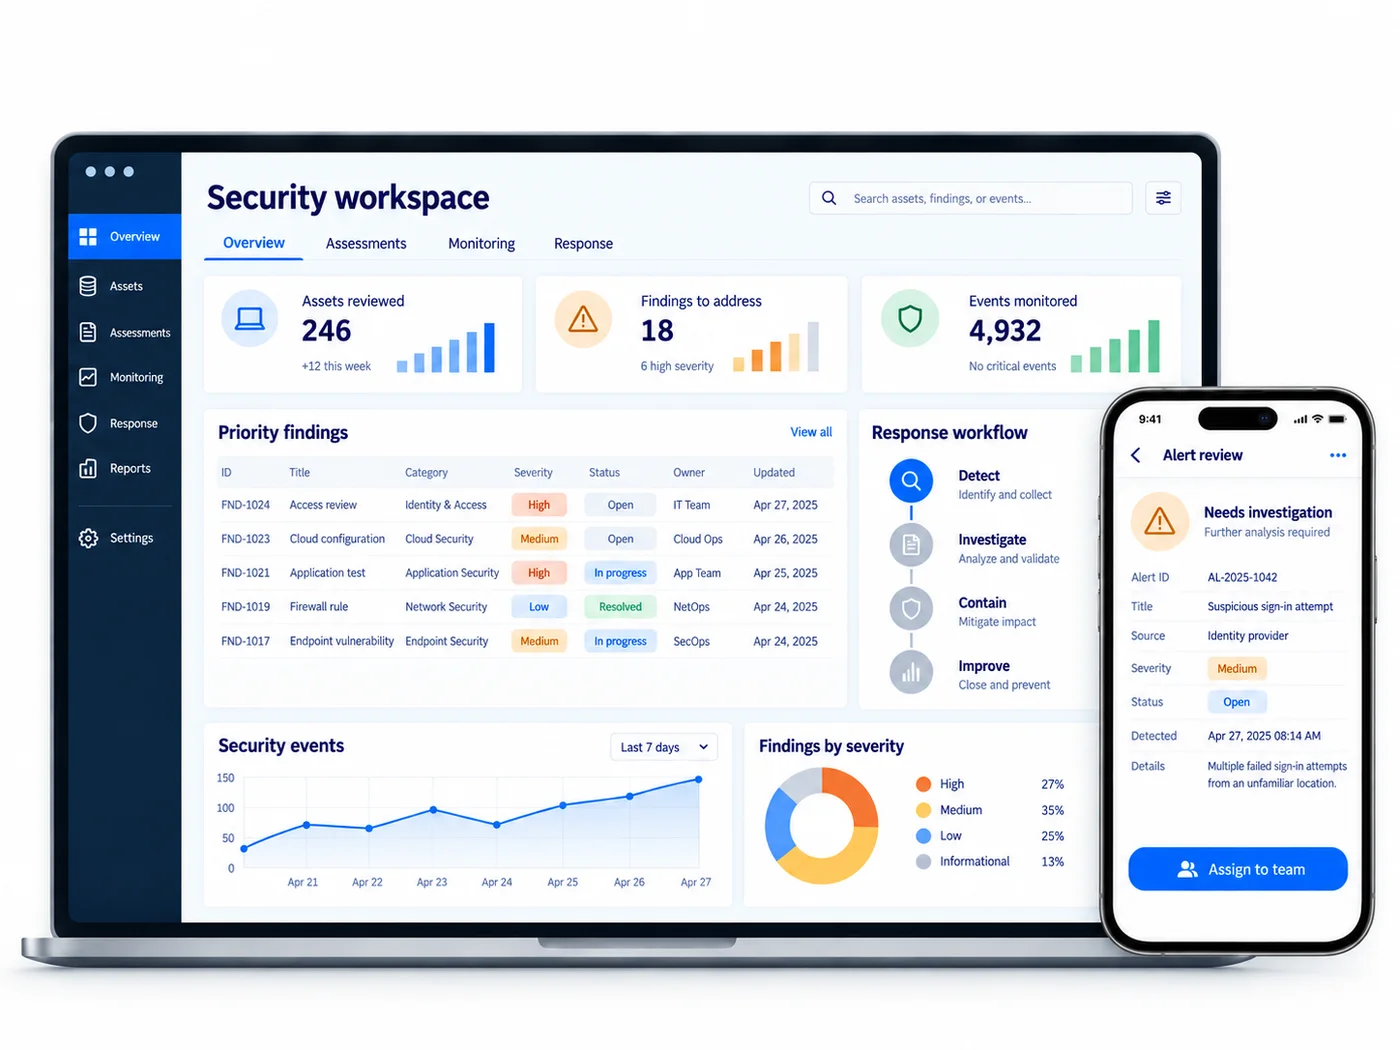
Security capabilities
Effective security connects assessment with action. We look at the systems you run, how they are used and the risks that matter most to your organization.
Review applications, infrastructure and working practices to identify exposure and set priorities.
Develop practical policies, responsibilities and risk frameworks that support how your organization operates.
Test agreed web applications, networks, cloud environments or wireless systems and provide actionable findings.
Identify, assess and track vulnerabilities, with guidance for validation, hardening and remediation.
Bring relevant security events together for monitoring, investigation and clearer reporting.
Connect signals across endpoints and systems to support detection, investigation and response.
Establish alert review, investigation and incident response workflows suited to the agreed scope.
Review identity, configuration, workloads and monitoring across AWS, Microsoft Azure and Google Cloud environments.
Security in focus
See the exposure.
Plan the response.
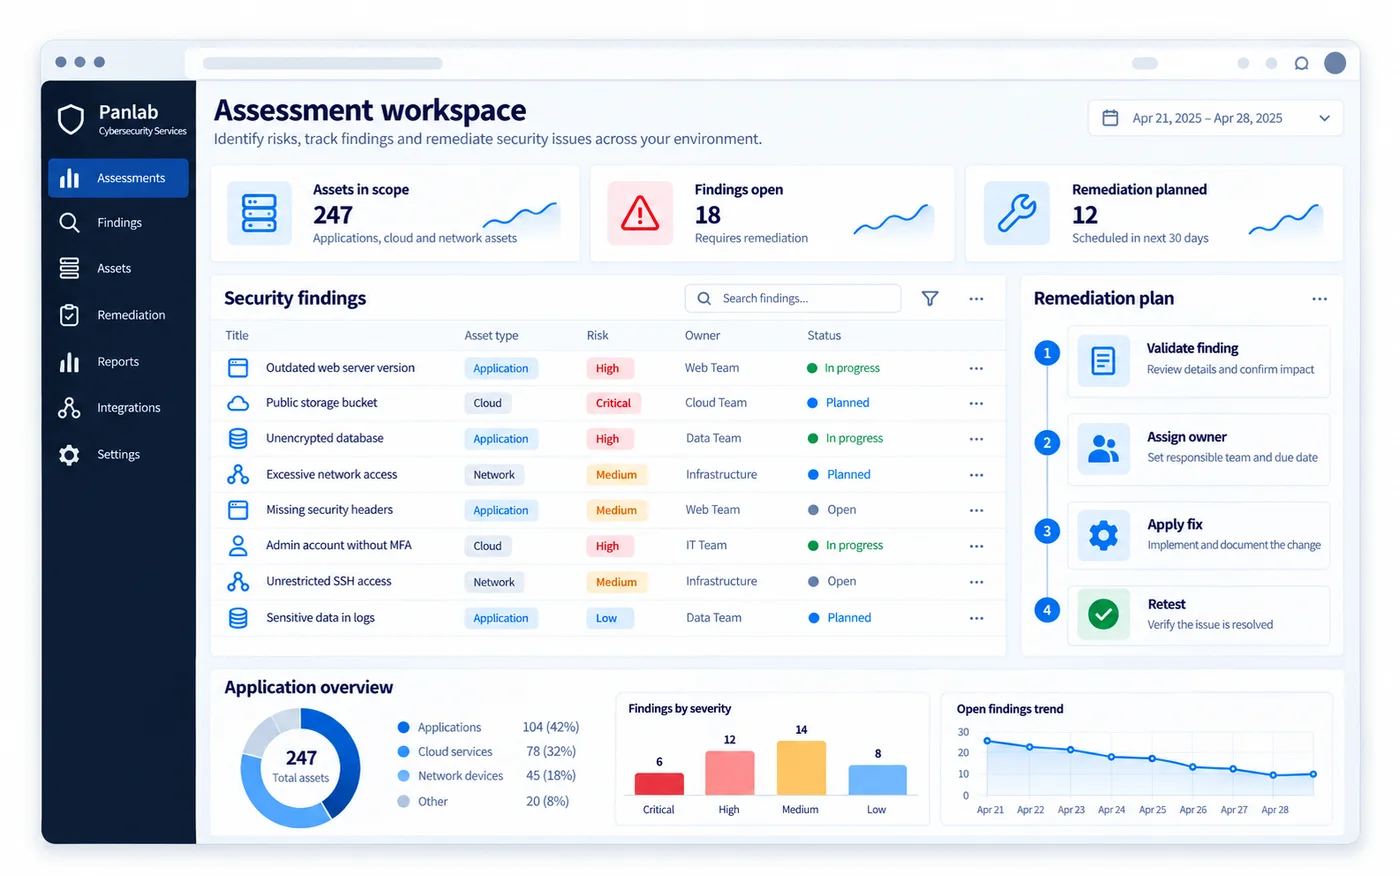
Assess systems, validate weaknesses and organize remediation around business impact and technical risk.
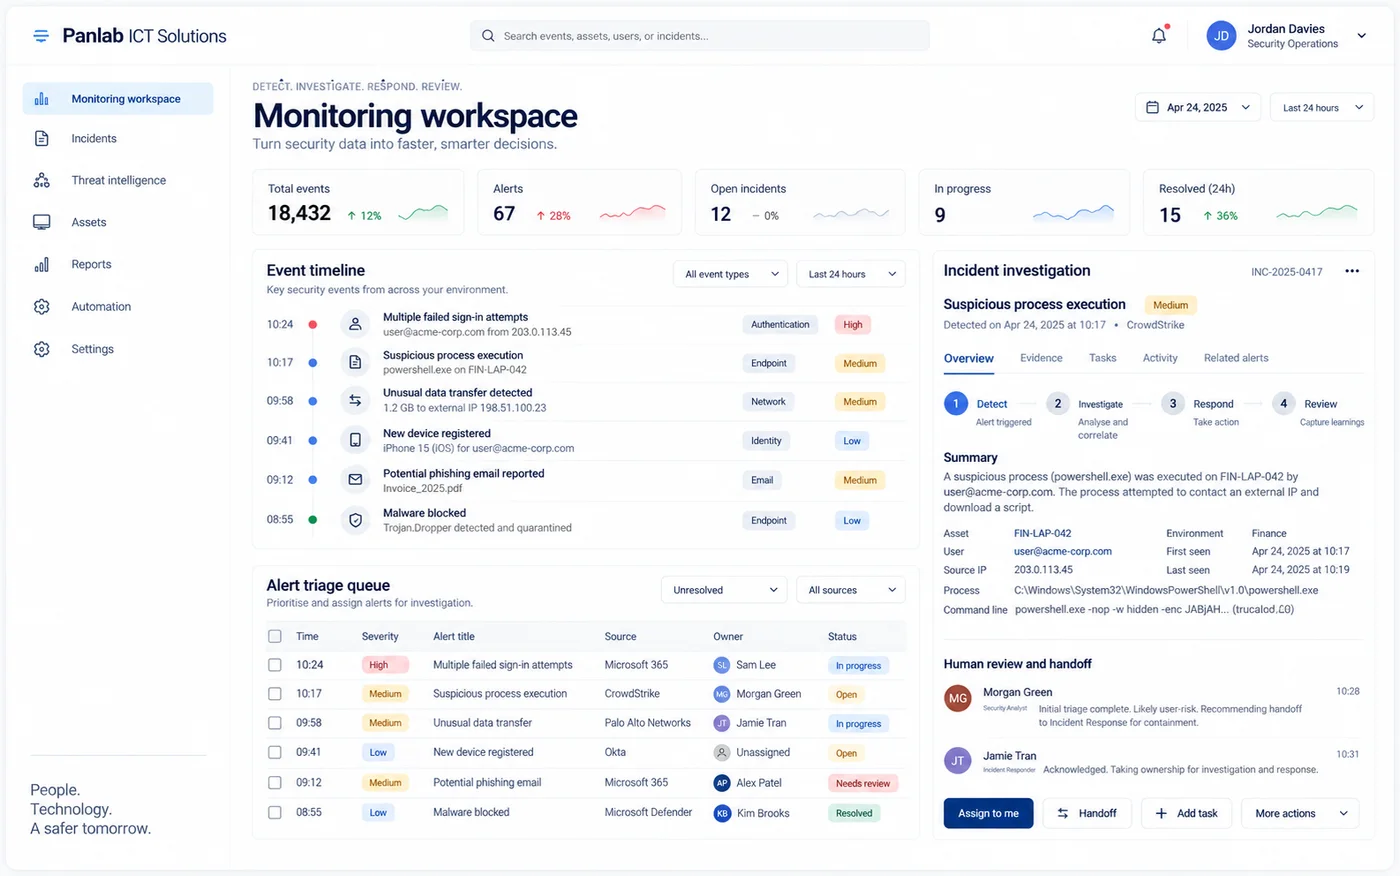
Bring security events and response steps into a clearer operational view, from initial alert to investigation and follow-up.
Our approach
We begin with your applications, infrastructure and operational priorities. The assessment then informs focused improvements and the monitoring or response processes that fit your environment.
Identify the systems, data, access and business processes that need protection.
Review risks and existing controls, then validate the most important findings.
Prioritize practical changes to configuration, applications, policies and response processes.
Use agreed signals and review cycles to keep visibility as the environment changes.
Established in India.
Working across borders.
Clients across
Cybersecurity FAQs
Tell us what systems you need to assess or protect. We’ll help define a sensible starting point and scope.
Talk with our teamDepending on the agreed scope, we can assess web applications, networks, cloud environments, wireless systems and related configurations, then provide prioritized findings and recommendations.
Yes. We can test an agreed environment for weaknesses, validate findings and provide remediation guidance. The test boundaries and methods are defined before work begins.
Yes. We can help bring relevant event sources into SIEM or XDR workflows for detection, investigation and reporting, based on the tools and systems in your environment.
We can help develop security policies, governance practices, risk assessments and compliance support appropriate to your organization. Specific regulatory or certification requirements are assessed as part of the engagement.
Yes. Monitoring can be paired with agreed alert handling, investigation and response steps so your team knows what to review and who should act when an issue arises.
Let’s strengthen what matters
Share your application, infrastructure or security challenge. We’ll discuss the scope and a practical way to begin.
Clearer risks.
Practical controls.
Better-informed response.